Tampilkan postingan dengan label log4j. Tampilkan semua postingan

Sabtu, 05 Maret 2022

43+ Log4j-core Vulnerability

43+ Log4j-core Vulnerability

In a statement the Cybersecurity and Infrastructure Security Agency on December 11 2021 called the log4j vulnerability a severe risk and offered this four-step guidance to patch Log4j and mitigate potential Log4Shell cyberattacks. 2 highlighting a critical remote code execution vulnerability in Log4j affecting versions between 20-beta9 to 2141.


04uxnkn6j Ylum
Known as Log4Shell the flaw is exposing some of.
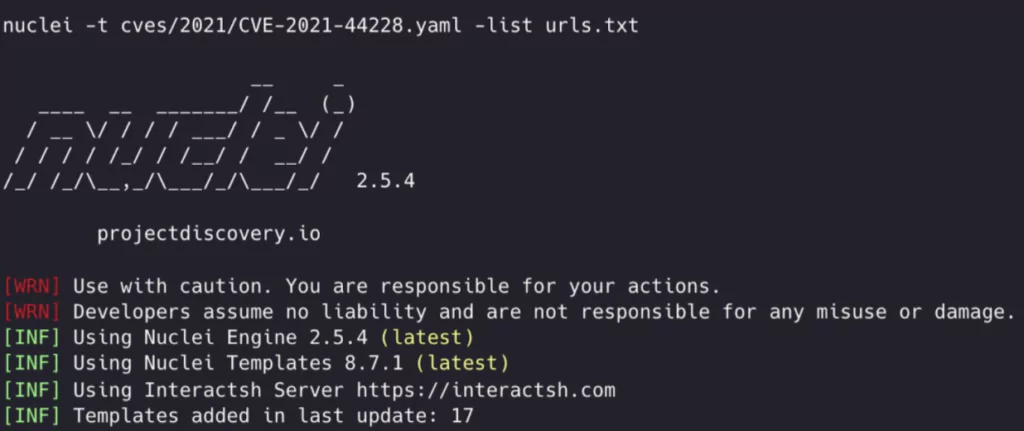
Log4j-core vulnerability. As it was vulnerable to illegitimate access by bad actors and hackers it is being anticipated that it might have been used to access data. This vulnerability allows an attacker to execute code on a remote server. Report new vulnerabilities Versions Report a new vulnerability.

On December 10 2021 a security vulnerability was identified in Apache Log4j 2 version 2141 or earlier CVE-2021-44228. Open-source reporting indicates that the critical vulnerability tracked as CVE-2021-44228. The vulnerability allows for unauthenticated remote code execution.

Today Dec10 2021 a new critical Log4j vulnerability was disclosed. Log4ShellThis vulnerability within the popular Java logging framework was published as CVE-2021-44228 categorized as Critical with a CVSS score of 10 the highest score possible. Security teams are working.

This vulnerability poses a risk to private data and the availability of your web server. Log4j 2 is an open source Java logging library developed by the Apache Foundation. This vulnerability is known as CVE-2021-44228 or as Log4Shell.

Apache Log4j is a library for logging functionality in Java-based applications Red Hat notes. To protect earlier releases of Log4j from 20-beta9 to 2100 the library developers recommend removing the JndiLookup class from the classpath. Spring by default uses the log4j-to-slf4j and log4j-api and you will be only affected if you have done some overriding to use the log4j-core.

As per the statement from the Springio team this vulnerability is affected only by the log4j-core library. Yesterday December 9 2021 a very serious vulnerability in the popular Java-based logging package Log4j was disclosed. Apache Log4j2 JNDI features do not protect against attacker controlled LDAP and other JNDI related endpoints For a description of this vulnerability see the Fixed in Log4j 2150 section of the Apache Log4j Security.

A critical vulnerability has been discovered in Apache Log4j 2 an open source Java package used to enable logging in many popular applications and it. Apache Log4j 2 utility is an open-source Apache framework that is used for logging requests. Description of the Vulnerability CVE-2021-44228.

Click the Installation in use and select. GOOGLE is warning users over a vulnerability that can be exploited by hackers. Log4J Vulnerability Overview On Friday 10th December Apache announced the discovery of a critical vulnerability in the Log4J logging library for Java which is used by millions of Java applications and other products and services to log error messages.

This does not include vulnerabilities belonging to this packages dependencies. Tracked as CVE-2021-44228 and by the monikers Log4Shell or LogJam the issue concerns a case of. This vulnerability has been resolved in Jamf Pro 10341.

The vulnerability known as Log4shell was identified in Apaches Log4j software library that helps developers keep track of changes in the applications they build. What is Log4J vulnerability. On December 9 2021 the following vulnerability in the Apache Log4j Java logging library affecting all Log4j2 versions prior to 2150 was disclosed.

Test and protect your applications Direct Vulnerabilities Known vulnerabilities in the orgapachelogginglog4jlog4j-core package. The vulnerability allows a remote unauthenticated actor to execute arbitrary code on an affected device. A vulnerability in the open source Apache logging library Log4j sent system administrators and security professionals scrambling over the weekend.

Go to the games launcher and open Installations. Jar org apache logging log4j core lookup JndiLookup class. Log4j is a Java package that is located in the Java logging systems.

Attackers are making thousands of attempts to exploit this severe vulnerability. The bug makes several online systems built on Java vulnerable to zero-day attacks. Zip -q -d log4j-core.

Log4j 2 is widely used in many applications and is present as a dependency in many services. Below is how to possibly fix the vulnerability of Minecraft versions from exploit log4j. The vulnerability known as Log4Shell affects Log4j an open-source logging library that developers use to track software activity in cloud and enterprise apps including Apples iCloud Twitter.

A critical vulnerability discovered in Log4j a widely deployed open-source Apache logging library is almost certain to be exploited by hackersprobably very soon. A so-called Remote Code Execution RCE. These include enterprise applications as well as numerous cloud services.

The vulnerability was discovered by Chen Zhaojun from Alibabas Cloud Security team. The vulnerability resides in the way specially crafted log messages were handled by the Log4j processor. It does not have the potential to impact managed computers directly.

Continuously find fix vulnerabilities like these in your dependencies. On December 10 2021 Apache released version 2150 of their Log4j framework which included a fix for CVE-2021-44228 a critical CVSSv3 10 remote code execution RCE vulnerability affecting Apache Log4j 2141 and earlier versions. Log4j flaw coverage what you need to know now.

For Apache log4j versions from 12 up to 1217 the SocketServer class is vulnerable to deserialization of untrusted data which leads to remote code execution if combined with a deserialization gadget. The Apache Software Foundation has released fixes to contain an actively exploited zero-day vulnerability affecting the widely-used Apache Log4j Java-based logging library that could be weaponized to execute malicious code and allow a complete takeover of vulnerable systems.

17+ Log4j Windows Server

17+ Log4j Windows Server

Still it looks like a time zone problem. Quick and dirty scanner using MD5 to ensure all Log4J locations are found even if re-named.


Simple Logging Facade For Java Slf4j Is An Abstraction Of Different Logging Frameworks Eg Log4j Java Util Logging Commons Logging Etc Facade Coding Java

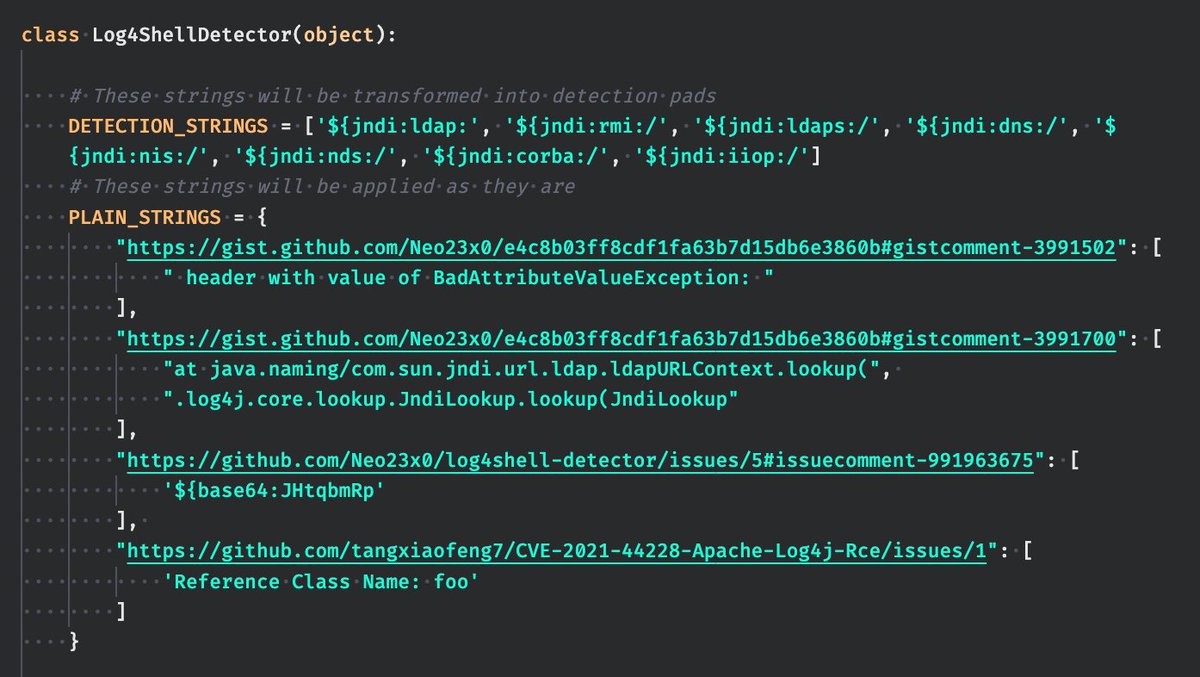
Note that this user input can be hidden in for instance the header of an HTTP call.

Log4j windows server. Log4j is used as a logging package in a variety of different popular software by a number of manufacturers including Amazon Apple iCloud Cisco Cloudflare ElasticSearch Red Hat Steam Tesla Twitter and video games such as Minecraft. Log4j 2 is a Java-based logging library that is widely used in business system development included in various open-source libraries and directly embedded in major software applications. 6 the vulnerable configurations have been disabled by default.

Apache Foundation Log4j 2 vulnerability CVE-2021-44228 CVE-2021-44228 also known as Log4Shell or LogJam is an unauthenticated RCE vulnerability that allows complete system takeover on systems with Log4j 20-beta9 to 2141 and it is being actively exploited. Step 1 Unzip and untar the. How to metigate Log4j Vulerability on Windows systems.

As delivered Log4j contains four ConfigurationFactory implementations. An example of such a class can be seen below. Security company offers Log4j vaccine for systems that cant be updated immediately.

A proof-of-concept exploit for the vulnerability now tracked as CVE-2021-44228 was published on December 9 while the Apache Log4j developers were still working on releasing a patched version. Posted by Vishnu Ashok December 12 2021 December 12 2021 Posted in Uncategorized windows Tags. The vulnerability tracked as CVE-2021-44228 and referred to as Log4Shell affects Java-based applications that use Log4j 2 versions 20 through 2141.

The vulnerability allows remote code execution on servers including those operated by Apple Twitter Valve Tencent and other. -DusertimezoneUTC and see if it anything changes. As of Log4j 2015 released on Dec.

Open-source projects like Paper the server used by Minecraft have begun patching Log4j 2. Published on GitHub on December 9 2021 the first proof-of-concept exploit enables. Log4j takes the default time zone so you could try running your application with the additional command line option.

To install log4j on your system download apache-log4j-xxxtargz from the specified URL and follow the steps give below. You can permanently close the vulnerability by causing the server to. Make sure you get these files from the main distribution directory rather than from a mirror.

This article assumes that you are familiar with Log4j and already using Log4j Sometimes we need the logs on different. Affecting everything from enterprise software to web applications and well-known consumer products CVE-2021-44228 impacts any organization using the Apache Log4j framework including Apache Struts2 Apache Solr Apache Druid Apache Flink and others. Dont you for example run the application on a different user account than you use for checking the date on the server.

Go to Start and right click on that then open System. When Log4j starts it will locate all the ConfigurationFactory plugins and arrange them in weighted order from highest to lowest. Log4j has the ability to automatically configure itself during initialization.

If you know that input is getting logged with log4j you can set up an LDAP server and return a compiled class file that executes some code. Servers used by such name companies as Twitter Cloudflare Apple and Tencent also have been found to be. The free version can let you log and index up to 500MG a day.

Log4j 2 is a popular Java logging framework developed by the Apache Software FoundationThe vulnerability CVE-2021-44228 allows for remote code execution against users with certain standard configurations in prior versions of Log4j 2. WindowsServer Log4j Scanner - Powershell CVE-2021-44228. Countless Servers Are Vulnerable to Apache Log4j Zero-Day Exploit.

The Log4j API supports lambda expressions. If it is exploited by bad actors it will allow remote. Go to Advanced Settings.

The Log4j API has several advantages over SLF4J. Apache crtical fix Java Log4j patch vulnerability windows. The bug makes several online systems built on Java vulnerable to zero-day attacks.

If attackers manage to exploit it on one of the servers they gain the ability to execute arbitrary code and potentially take full control of the system. As it was vulnerable to illegitimate access by bad actors and hackers it is being anticipated that it might have been used to access data. One for JSON one for YAML one for properties and one for XML.

This object sends my etcpasswđ file to an external URL using curl. The system is logging and appears to be adhering to the MaxFileSize limit as defined in the log4jproperties 20KB - see below but is not rolling the log files. CVE-2021-44228 also named Log4Shell or LogJam is a Remote Code Execution RCE class vulnerability.

First download the KEYS as well as the asc signature file for the relevant distribution. Rather it is simply overwriting the existing log file. Windows 11 5G Best VPNs Cloud.

You can also get splunk to monitor other logs on various machines so you can quicky identify what changes just before your application started to throw errors. The Log4j API is a logging facade that may of course be used with the Log4j implementation but may also be used in front of other logging implementations such as Logback. In order to mitigate vulnerabilities users should switch log4j2formatMsgNoLookups to true by addingDlog4j2formatMsgNoLookupsTrue to the JVM command for starting the application.

Log4j is used in numerous Java applications and is present in many services as a. Then verify the signatures using gpg --import KEYS gpg --verify apache-log4j-2141-bintargzasc Apache Log4j 2141 is signed by Ralph Goers B3D8E1BA. Log4j is a very popular package for logging purpose written in Java.

The Log4j API supports logging Messages instead of just Strings. Log4j is a Java package that is located in the Java logging systems.

Jumat, 25 Februari 2022

47+ Log4j-over-slf4j

47+ Log4j-over-slf4j

Log4j2 and SLF4j Binding Dependencies. It is simple yet flexible and allows for readability and performance improvements.


Simple Logging Facade For Java Slf4j Is An Abstraction Of Different Logging Frameworks Eg Log4j Java Util Logging Commons Logging Etc Facade Coding Java

Introduction to Slf4j and Log4j.

Log4j-over-slf4j. Log4j implemented over SLF4J License. Can we do this upgrade with the spring version. To make Log4j2 work with SLF4J we need to include the following 3 dependencies.

Logging bridge apache slf4j. SLF4J helps with the silent switching between logging frameworks. In addition were referencing two other projects dedicated to different articles but containing discussed log configurations here and here.

We are using log4j-over-slf4j-1725 JAR. Comparison SLF4J and Log4j Unlike log4j SLF4J S imple L ogging F acade for J ava is not an implementation of logging framework it is an abstraction for all those logging frameworks in Java similar to log4J. Log4j is a specific log system.

Due to a break in compatibility in the SLF4J binding as of release 2111 two SLF4J to Log4j Adapters are provided. There is a new version for this artifact. The Apache Log4j binding between Log4j 2 API and SLF4J.

We wanted to upgrade to log4j-slf4j-impl-20jar. Gradle Short Gradle Kotlin SBT. As usual the code can be found over on GitHub.

Following are the reasons which are good enough to choose SLF4J over Log4j. Log4j 2 is broken up in an API and an implementation core where the API provides the interface that applications should code to. The Log4j API supports logging Messages instead of just Strings.

The Log4j API supports lambda expressions. Follow asked 1 min ago. Slf4j-api is the basic API slf4j-log4j12 routes the actual logging to Log4J jcl-over-slf4j intercepts Commons Logging and routes it through SLF4J to Log4J log4j will be your physical logging framework Im assuming that you already have configuration for Log4J andor are comfortable writing that configuration.

This warning message is. The Log4j API is a logging facade that may of course be used with the Log4j implementation but may also be used in front of other logging implementations such as Logback. For Log4j 2 to SLF4J you will have to add Log4j 2 to SLF4J Adapter.

Date Dec 10 2021 Files. SLF4j provides place holder based logging which improves readability of code by removing checks like isDebugEnabled isInfoEnabled etc. It allows applications coded to the SLF4J API to use Log4j2 as the implementation.

Log4j-slf4j-impljar Log4j 2 SLF4J binding. Central 72 Redhat GA 8 Redhat EA 4 JBoss 3rd-party 3. Initialize Log4j through slf4j-log4j12 to achieve the final log output.

It is always better to use abstraction. These replacement classes redirect all work to their corresponding SLF4J classes. Failed to load class orgslf4jimplStaticLoggerBinder.

The reason why Log4j 2 is still using its own configuration is because you are only using SLF4Js log4j-over-slf4j which is for Log4j 1 despite not being that clearly documented. SLF4j Vs Log4j Which One is Better. Slf4j-log4j12 is an adapter linking slf4j-api and log4j.

It is only an abstraction layer to an underlying logging component. 73 rows Log4j implemented over SLF4J License. The Apache Log4j binding between Log4j 2 API and SLF4J.

If you do you will get the following exception. Logback does NOT offer a lookup mechanism at the message level. Therefore you cannot have both in the classpath.

It is not a logging component and it does not do the actual logging. Click on the respective links to get the latest version of each. In simple terms we can say that Slf4j is a simple logging facade for Java.

Therefore you cannot compare both. The Log4j 2 SLF4J Binding allows applications coded to the SLF4J API to use Log4j 2 as the implementation. It implements the StaticLoggerBinder interface in slf4j-api so that the getSingleton method of slf4j-log4j12 is bound at compile time.

Name Email Dev Id Roles Organization. SLF4J is an open-source library or internal library that makes it independent of any particular logging implementation which means no need to manage multiple logging configurations for multiple libraries. Detected both log4j-over-slf4jjar AND bound slf4j-log4j12jar on the class path.

Central 66 Redhat GA 7 Redhat EA 4 JBoss 3rd-party 3. However it is always difficult to prefer one between the two. To redirect the log4j logger calls to slf4j you need to use log4j-over-slf4jjar binding and if you want to redirect slf4j calls to log4j you need to use slf4j-log4j12jar binding.

Strictly speaking Log4j core is only needed at runtime and not. If you are using log4j-over-slf4jjar with SLF4J API you are safe unless the underlying implementation is log4j 2x. The log4j-over-slf4j module contains replacements of most widely used log4j classes namely orgapachelog4jCategory orgapachelog4jLogger orgapachelog4jPriority orgapachelog4jLevel orgapachelog4jMDC and orgapachelog4jBasicConfigurator.

Does a similar vulnerability exist in logback. Java spring log4j log4j2 slf4j. The Log4j API has several advantages over SLF4J.

Log4j-slf4j-impl should be used with SLF4J 17x releases or older. Also any guidance on this migration would be really helpful. However we are still looking at other possible vulnerabilities of lesser severity.

Pom 6 KB jar 17 KB View All. So also we can say that Slf4j and log4j are like abstraction class and interface in Java. Apache Log4j to SLF4J Adapter 2150.

Detected both log4j-over. Thus it is deemed safe with respect to CVE-2021-44228.

Kamis, 03 Februari 2022

36+ Log4j Kibana

36+ Log4j Kibana

That gave us. This vulnerability is identified as a zero-day vulnerability.


Logstash Plugins Elk Plugins Dots

Is it best to change each log4jxml file to append to single logstash agent on the local host 1 to 1 mapping that in turn pushes to ElasticSearch on the remote host where Kibana is running.

Log4j kibana. The Apache Software Foundation has released fixes to contain an actively exploited zero-day vulnerability affecting the widely-used Apache Log4j Java-based logging library that could be weaponized to execute malicious code and allow a complete takeover of vulnerable systems. Get started docker-compose up Sample log4j configuration. The list above is available on our GitHub Gist.

I have 12 log log4j files I want to be indexed in LogstashKibana. Logging using Elasticsearch Logstash and Kibana There are various approaches with different trade-offs for ingesting logs into an ELK stack. These include enterprise applications as well as numerous cloud services.

Its a graylog. At this time CVE-2021-4101 has been designated for the impact to Log4j 1x. Tracked as CVE-2021-44228 and by the monikers Log4Shell or LogJam the issue concerns a case of.

Orggraylog2log4j2 log4j2-gelf 132 Reviews. Every other security measure TLS RBAC etc has been made obsolete and even 716 is affected because log4j 2111 is included. The vulnerability allows remote code execution on servers including those operated by Apple Twitter Valve Tencent and other.

Easily share Kibana visualizations with your team members your boss their boss your customers compliance managers contractors anyone you like really using the sharing option that works for you. I found solution that fits my requirements most. Logging using Elasticsearch Logstash and Kibana There are various approaches with different trade-offs for ingesting logs into an ELK stack.

Log4j Configuration Log4j provides a multitude of JSON generating layouts. There was an advisory CVE-2021-44228 on a critical vulnerability found on log4j2 the most common logging library used in Java applications worldwide developed by Apache Software Foundation. Countless Servers Are Vulnerable to Apache Log4j Zero-Day Exploit.

If you know how it works its simple but maybe someone else can benefit from the hours I spent looking into this. How to connect log4j with Logstash ElasticSearch and Kibana With several log4j configurations you can monitor your logs with ELK. To use it I added this dependency along with basic log4j2 dependencies.

Log4J is often installed on both Linux and Windows systems either directly or often as a requirement of another package or system. Risks Mitigation and fixes on Java Spring Boot Applications. Use the log4j2 SocketAppender to log to logstashkibana via SSLTLS.

Configuring log4j for writing to local files edit In your log4jproperties file remove SocketAppender and replace it with RollingFileAppender. Log4j 2 is widely used in many applications and is present as a dependency in many services. Java log4j2 logging logstash kibana tcp socket ssl tls.

Embed a dashboard share a link or export to PDF PNG or CSV files and send as an attachment. Normally you can use the images for Kibana and Elasticsearch direct without to build the image with a Dockerfile. In Kibana the logs appear as if they came from the sidecar container of the same pod.

Configure your log4jproperties in your app to write to a local file. Btw once we upgrade to Karaf 41 we will also switch from log4j to log4j2 so any implementation that only works on log4j would b. It indeed might be tricky as it will depend on the used logging framework and Karaf leaves some choices to the user.

It is not compatible with Tenableio cloud scanners and may fail to return results in certain networks due to firewall rules or interference from other security devices. Here we will briefly cover how one can forward Log4j generated events first to Logstash and then to Elasticsearch. Log4j is a Java package that is located in the Java logging systems.

This also counts for Logstash. Log4j Configuration Log4j provides a multitude of JSON generating layouts. Callback Domains log4j.

Forward Log4j 2 logs to the applications stdout By streaming application logs to its own stdout the Liberty server logs are separated from the application logs. Initially there were mixed reports GitHub Original Post as to the susceptibility of Log4j 1x. This article describes how to setup the log4j2 SocketAppender in an SSLTLS context.

So 12 logstash agents on the app server. If it is exploited by bad actors it will allow remote code execution RCE and allow to download of. The bug makes several online systems built on Java vulnerable to zero-day attacks.

Creating the keystore with. Install and configure filebeat to collect those logs and ship them to Logstash Configure Logstash to use the beats input. Plugin ID 155998 - Apache Log4j Message Lookup Substitution RCE Log4Shell Direct Check - This plugin listens for an LDAP BIND connection from a target host.

As it was vulnerable to illegitimate access by bad actors and hackers it is being anticipated that it might have been used to access data. The following projects dont appear to use Log4j by default though they may optionally be configured to use it. Since its build based on elasticsearch the usage is familiar so I was able to switch to it immediately.

Here we will briefly cover how one can forward Log4j generated events first to Logstash and then to Elasticsearch. Meanwhile we have added -Dlog4jformatMsgNoLookupstrue to the jvmoptions file and the rolling upgrades are running. At 1010 severity this is comfortably one of the most serious IT.

Like Heartbleed and Shellshock we suspect the number of vulnerable environments to grow over the coming weeks. We continue to explore options for additional detection and. Configure a Log4j 2 Appender to send your logs to a File or RollingFile.

Elastic has meanwhile provided detailed information about the impact for their products. Instantly share code notes and snippets. This vulnerability is known as CVE-2021-44228 or as Log4Shell.

Probably best to ask at the Karaf forum if people have a UI for log level management.

Kamis, 06 Januari 2022

35+ Log4j Exploit

35+ Log4j Exploit

Logging lets developers see all the activity of an application. If exploited the vulnerability allows remote code execution on vulnerable servers giving an attacker the ability to import malware that would completely compromise machines.


Virusom Flashback Je Stale Nakazenych Priblizne 100 000 Macov On Http Www Macweb Sk Virusom Flashback Je Stale Java Tutorial Design Patterns In Java Tutorial

12102021 Gabriel Gabor Andre Bluehs A zero-day exploit affecting the popular Apache Log4j utility CVE-2021-44228 was made public on December 9 2021 that results in remote code execution RCE.

Log4j exploit. There is a patch available and you should patch immediately. This vulnerability is actively being exploited and anyone using Log4j should update to version 2150 as soon as possible. What you need to know.

At the time of writing exploit attempts lead to commodity cryptominer payloads. Earliest evidence weve found so far of Log4J exploit is 2021-12-01 043650 UTC Cloudflare CEO Matthew Prince said on Twitter. Proof-of-concept exploits for a critical zero-day vulnerability in the ubiquitous Apache Log4j Java-based logging library are currently being shared online exposing home users and enterprises.

The exploit lets an attacker load arbitrary. Those coming from input. The vulnerability is dubbed Log4Shell and is officially CVE-2021-44228 CVE number is the unique number given to each vulnerability discovered across the world.

A critical vulnerability has been discovered in Apache Log4j 2 an open source Java package used to enable logging in many popular applications and it. Ars Technica reports that the log4j exploit comes from a malicious code on servers or clients running the Java version of Minecraft. A so-called Remote Code Execution RCE.

Exploit proof-of-concept code is widely available and internet wide scanning suggests active exploitation. On December 10 2021 Apache released version 2150 of their Log4j framework which included a fix for CVE-2021-44228 a critical CVSSv3 10 remote code execution RCE vulnerability affecting Apache Log4j 2141 and earlier versionsThe vulnerability resides in the way specially crafted log messages were handled by the Log4j processor. The bug tracked as CVE-2021-44228 is a.

However convenient features often involve potential security issues at the same time. The log4j library is a powerful log framework with very flexible features supported. This vulnerability is actively being exploited in the wild allows remote code execution and is trivial to exploit.

Without careful user input filtering and strict input data sanitization a blind. Log4j 2 developed by the ASF is a widely used Java package that enables logging in an array of popular applications. At the time of receiving these reports the vulnerability apparently has been exploited by threat actors in the wild and no patch was available to fix the.

They report that it. Yesterday December 9 2021 a very serious vulnerability in the popular Java-based logging package Log4j was disclosed. CVE-2021-44228 is a Remote.

The vulnerability affects Apache Log4j between versions 20 and 2141 and at the time of writing there have already been reports of it being successfully exploited on some Java 11 runtimes. The problem impacts Log4j 2 versions which is a very common logging library used by applications across the world. All an attacker has to do to exploit the flaw is strategically send a malicious code string that eventually gets logged by Log4j version 20 or higher.

Due to the severity of impact from the exploit RCE. Attackers are actively exploiting a critical vulnerability in Apache Log4j a logging library thats used in potentially millions of Java-based applications including web-based ones. Security A newly discovered zero-day vulnerability in the widely used Java logging library Apache Log4j is easy to.

This vulnerability allows an attacker to execute code on a remote server. Microsoft said Saturday that exploits so far of the critical Apache Log4j vulnerability known as Log4Shell extend beyond crypto coin mining and into more serious territory such as credential and. What is the Minecraft log4j exploit.

On Friday morning NCSCGovCERTch received reports about a critical vulnerability in a popular Java library called Log4j. A newly discovered zero-day vulnerability in the widely used Java logging library Apache Log4j is easy to exploit and enables attackers to gain full control of affected servers. A vast majority of the exploitation attempts against Log4Shell have originated in Russia 4275 based on.

That suggests it was in the wild at least 9 days before. On December 10 2021 Topic. In a sign that the threat is rapidly evolving Check Point researchers cautioned of 60 new variations of the original Log4j exploit being introduced in less than 24 hours adding it blocked more than 845000 intrusion attempts with 46 of the attacks staged by known malicious groups.

Digging deeper into Log4Shell - 0Day RCE exploit found in Log4j. The Log4j exploit that has seen software providers and anti-virus companies alike warning over the potential damage it could cause have warned that the exploit has moved from focusing on cryptojacking to data theft infected machines. Our next-gen WAF customers can enable a templated rule to protect themselves from this vulnerability.

Following the acknowledgement of products affected by Log4j Randori can confirm the exploitability of Jamf Pro security notice via the Log4j CVE-2021-44228 also known as Log4Shell Recent unpatched versions of Jamf Pro including those running on Java 11 are not and should not be considered protected against this exploitation. A new critical remote code execution vulnerability in Apache Log4j2 a Java-based logging tool is being tracked as CVE-2021-44228. Zero-Day Exploit Targeting Popular Java Library Log4j.

Minggu, 02 Januari 2022

16+ Log4j Vulnerability Jar

16+ Log4j Vulnerability Jar

The log4j vulnerability parses this and reaches out to the malicious host via the Java Naming and Directory Interface JNDI. Similarly to other high-profile vulnerabilities.


Mn 6vk13hcaimm

The vulnerability also impacts Adobe ColdFusion.

Log4j vulnerability jar. These are the sorts of vulnerabilities that could be. On December 10 2021 a security vulnerability was identified in Apache Log4j 2 version 2141 or earlier CVE-2021-44228. CVE-2021-44228 is a remote code execution RCE vulnerability in Apache Log4j 2.

Pega software can use the Log4j component in two. Reports of a Minecraft log4j exploit have surfaced with players sharing how to fix the vulnerability of java versions 17 to 118. A new critical remote code execution vulnerability in Apache Log4j2 a Java-based logging tool is being tracked as CVE-2021-44228.

This gives an attacker the ability to run any code they would like on the target the. Adobe is investigating any potential impact and is taking action including updating affected systems to the latest versions of Apache Log4j recommended by the. Yesterday the Apache Foundation released an emergency update for a critical zero-day vulnerability in Log4j a ubiquitous logging tool included in almost every Java application.

As it was vulnerable to illegitimate access by bad actors and hackers it is being anticipated that it might have been used to access data. There is a critical security vulnerability CVE-2021-44228 in the Log4j which is a popular logging library for Java-based applications. The Apache Logging Services team provides the following mitigation advice.

Threat actors are actively weaponizing unpatched servers affected by the newly identified Log4Shell vulnerability in Log4j to install cryptocurrency miners Cobalt Strike and recruit the devices into a botnet even as telemetry. The bug makes several online systems built on Java vulnerable to zero-day attacks. The vulnerability affects multiple versions of Log4j 2.

This vulnerability was discovered by Chen Zhaojun of Alibaba Cloud Security Team. Log4j versions 20 through 2141 have been found to be vulnerable to a Remote Code Execution vulnerability due to the fact JNDI does not protect against attacker-controlled directory service providers. Yesterday December 9 2021 a very serious vulnerability in the popular Java-based logging package Log4j was disclosed.

A so-called Remote Code Execution RCE. The crafted request uses a Java Naming and Directory Interface JNDI injection via a variety of services including. 10 CVE-2021-44228 in the Apache Log4j logging software.

The vulnerability was discovered by Chen Zhaojun from Alibabas Cloud Security team. To build a custom vulnerability detection rule open Prisma Cloud and navigate to the following page. This was designed to make a JNDI call to substitute some information from a remote resource if a particular format of the log was found.

CVE-2021-44228 also identified as Log4Shell is a critically rated vulnerability impacting Log4j 2 Java log manager which is integrated into Apaches web server suite. The issue has been. What is Log4J vulnerability.

Apache Log4j is part of the Apache Logging Project. December 12 2021 Ravie Lakshmanan. Description of the CVE-2021-44228 vulnerability.

The Log4j JAR can be directly included in our project or it can be hidden away in one of the dependencies we include. The Log4j software is ubiquitously used by most organizations around the world. If your organization deploys or uses Java applications or hardware running Log4j 2x your organization is likely affected.

The recent vulnerability is identified and affected on the 2x version of log4j primarily. An unauthenticated remote attacker could exploit this flaw by sending a specially crafted request to a server running a vulnerable version of log4j. Due to this deployment methodology the impact is difficult to quantify.

Apache Log4j Vulnerability Log4Shell Widely Under Active Attack. For example using Syft to. Because of the widespread use of Java and log4j this is likely one of the most serious vulnerabilities on the Internet since both.

By and large usage of this library is one of the easiest ways to log errors and that is why most Java developers use it. Additionally Prisma Cloud users can also build a custom vulnerability detection rule to identify if any system is running a vulnerable Log4j package or JAR file with a version equal to or older than 2141. Remediating the Log4J Vulnerability.

10 Dec 2021 350 pm. Typical CVE-2021-44228 Exploitation Attack Pattern. This issue was fixed in Log4J v2150.

The Log4j 2 library is very frequently used in enterprise Java software. This vulnerability poses a risk to private data and the availability of your web server. In previous releases 210 this behavior can be mitigated by setting system property log4j2formatMsgNoLookups to true or by removing the JndiLookup class from the classpath example.

This vulnerability could allow malicious actors to take control of organizational networks using Log4j. Log4ShellThis vulnerability within the popular Java logging framework was published as CVE-2021-44228 categorized as Critical with a CVSS score of 10 the highest score possible. A zero-day vulnerability was identified on Friday Dec.

Analysis and Remediation Guidance to the Log4j Zero-Day RCE CVE-2021-44228 Vulnerability. If it is exploited by bad actors it will allow remote. Mitigating the Apache Log4j 2 Vulnerability.

Staying Secure Apache Log4j Vulnerability. Zip -q -d log4j-core. Log4j is a Java package that is located in the Java logging systems.

A vulnerability rated with a Critical impact is one which could potentially be exploited by a remote attacker to get Log4j to execute arbitrary code either as the user the server is running as or root. It impacts Apache Log4j 2 versions 20 through 2141 Apache is nearly ubiquitous. A high severity vulnerability and proof of concept was released today for a vulnerability in Apache.

Log4J 2x version has got an option called message lookup substitution. A critical vulnerability has been discovered in Apache Log4j 2 an open source Java package used to enable logging in many popular applications and it can be exploited to. Today Dec10 2021 a new critical Log4j vulnerability was disclosed.

A previously unknown zero-day vulnerability in Log4j 2x has been reported on December 9 2021. The first-stage resource acts as a springboard to another attacker-controlled endpoint which serves Java code to be executed on the original victim. The vulnerability allows for remote code execution as the user running the application that utilizes the library.

What is Apache Log4J and why is this library is so popular. Log4j 2150 has been released which no longer has this vulnerability. As the POC published on GitHub points out when log4j logs an attacker-controlled string value it.

This vulnerability allows an attacker to execute code on a remote server. It does not have the potential to impact. Exploit proof-of-concept code is widely available and internet wide scanning suggests active exploitation.